Cyber Threat Intelligence
Cyber Attack News
Today's cyber attacks, data breaches and hacking news, from ransomware crews to state-backed intrusions and law-enforcement takedowns. Every story is reported from official government advisories and analysed for what defenders should do next.
All attack news
-
ACTIVE EXPLOITATION
CISA flags exploited vCenter, Roller, Expressway and SAP portal flaws
CISA added four exploited flaws to KEV on 20 November: VMware vCenter, Apache Roller, Cisco Expressway and SAP NetWeaver. All carry a 23 November deadline.
-
 ACTIVE EXPLOITATION
CISA flags exploited Synology, LiteLLM, Apache Axis and REDCap flaws
CISA added four exploited flaws to KEV on 18 November: Synology DSM, LiteLLM, Apache Axis 1.x and REDCap. Three carry a 21 November deadline and a compromise check.
-
 LAW ENFORCEMENT
UK national gets six years for SMS phishing and SIM-swap crypto thefts
A UK national received 72 months for a smishing and SIM-swap conspiracy that breached at least 12 companies and stole $11.6 million in crypto from US victims.
-
 ADVISORY
Australia warns some flaws are exploited within 48h of patches
ASD rates its new patching alert critical: some flaws were exploited within 48 hours of fixes and reported CVEs rose 30%. What defenders should change first.
-
 ACTIVE EXPLOITATION
CISA flags exploited Puppet Enterprise report deserialization flaw
CISA added a Puppet Enterprise report deserialization bug to its KEV catalog. Any agent certificate can run code on the Puppet Server; patch by 1 December.
-
 ADVISORY
CISA urges immediate patching of Java HotSpot Base64 decoder flaw
CISA and Canada's Cyber Centre warn that crafted Base64 input can crash the Java HotSpot JVM and may allow remote code execution. Find every bundled runtime.
-
 SUPPLY CHAIN
Two agent-framework releases on PyPI shipped a CI credential stealer
PyPI agent-framework 1.26.1 and 1.26.2 ran a credential stealer on install, aimed at cloud, CI and GitHub Actions tokens. Rotate secrets if you pulled them.
-
 MALWARE
FBI FLASH: Gootloader hijacks WordPress to snare legal professionals
An FBI FLASH details how Gootloader poisoned search results through 1,000+ hacked WordPress sites to reach lawyers, a ransomware precursor tied to $28M paid.
-
 ACTIVE EXPLOITATION
Exploited UnrealIRCd and Check Point Gaia flaws get 3-day KEV deadline
CISA flagged an UnrealIRCd server-command injection and a Check Point Gaia root socket flaw as exploited, set a 16 November due date and asked for compromise checks.
-
 ADVISORY
FBI warns attackers are automating intrusions with ARTEX agentic AI tool
An FBI FLASH says actors have used the open-source ARTEX framework since August 2026 to automate breaches, some reaching privileged access within three hours.
-
 LAW ENFORCEMENT
Gootloader botnet disrupted: 100+ servers cleaned, domains seized
US and allied police cleaned more than 100 servers, including hacked WordPress sites, and seized domains behind Gootloader, a loader linked to ransomware losses.
-
 NATION-STATE
FBI: North Korean "FaceStealer" fake video calls drained $400M
An FBI FLASH attributes a $400M crypto theft campaign to North Korean state hackers who replay victims’ stolen webcam footage in fake meetings to infect new targets.
-
 ACTIVE EXPLOITATION
Barracuda appliance flaw chain tops six new CISA KEV additions
CISA added six exploited flaws to KEV on 10 November, including two chainable Barracuda bugs with a 13 November deadline and a Chromium use-after-free.
-
 ACTIVE EXPLOITATION
CISA flags exploitation of GPUStack, FreeSWITCH, Aspera, OpenSSH bugs
CISA added four flaws to its exploited-vulnerabilities catalog: auth bypasses in GPUStack, IBM Aspera Faspex and OpenSSH on musl Linux, plus FreeSWITCH command execution.
-
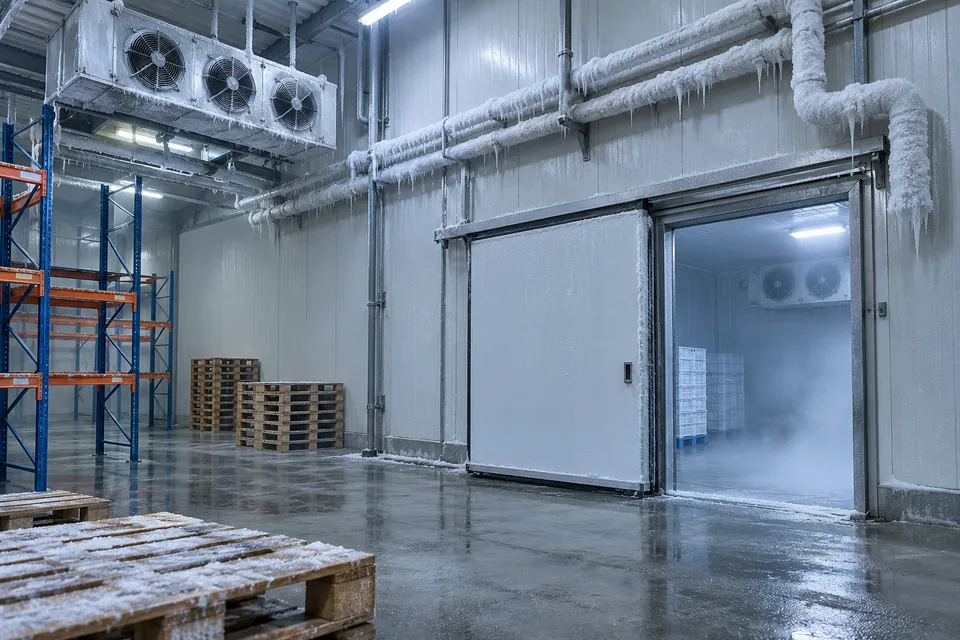 ADVISORY
US agencies warn of targeting of cold-chain refrigeration controllers
Five US agencies say hackers are targeting refrigeration controllers and may force heating cycles that spoil stock. The factsheet lists eight defensive steps.
-
 ADVISORY
UK cyber agency sees AI-enabled intrusion scaling through 2028
NCSC scenario assessment expects AI cyber tools to speed UK intrusions, targeting legacy critical systems. It flags patch and testing speed as a pressure point.
-
 LAW ENFORCEMENT
Ransomware affiliate for Nefilim and Hive gets 70 months in US prison
A Ukrainian national who worked as an affiliate for the Nefilim and Hive ransomware groups was sentenced to 70 months after ransomware attacks on healthcare providers and law firms.
-
 ACTIVE EXPLOITATION
CISA flags exploited flaws in Brotli, Magento, ESX and Linux
CISA added four exploited bugs to KEV in two days: Brotli, Adobe Commerce and Magento, VMware ESX and the Linux kernel. Brotli has the widest exposure.
-
 ACTIVE EXPLOITATION
PHP "php2shell" flaws now exploited, CISA sets a three-day deadline
CISA moved both php2shell PHP flaws into its KEV catalog on 26 October, giving federal agencies until 29 October to patch and to check for prior compromise.
-
 ACTIVE EXPLOITATION
Exploited Nextcloud CODE server and VeloCloud flaws get 3-day KEV deadline
CISA listed an exploited command injection in the Collabora CODE app for Nextcloud and a VeloCloud Orchestrator SQL injection, both due 26 October with triage.
-
 ADVISORY
Two critical PHP flaws could allow unauthenticated code execution
CISA, the UK NCSC and the FBI urge immediate patching of two critical PHP core flaws that could allow remote code execution on web-facing servers.
-
 ACTIVE EXPLOITATION
Exploited Zammad helpdesk chain runs from session hijack to root
CISA added two chained Zammad flaws to its KEV catalog: a session hijack giving code execution and a local root escalation, with a 5 October federal deadline.
-
 LAW ENFORCEMENT
Two get 189 months combined for US business email wire-fraud scheme
Two Delaware men who phished business mailboxes and redirected wires, including a $1.68M payment, got 189 months combined. What finance teams should change.
-
 ACTIVE EXPLOITATION
Exploited FortiMail flaw lets attackers write files with no fix out yet
CISA added an unauthenticated FortiMail path traversal to its KEV catalog with a three-day deadline and a compromise check, while fixed builds are still pending.
-
 ACTIVE EXPLOITATION
Apple CoreGraphics zero-day exploited in targeted attacks, CISA says
CISA added an Apple CoreGraphics memory flaw to its KEV catalog after reports of targeted attacks, with a 2 October deadline and forensic triage for iOS and macOS.
-
 ACTIVE EXPLOITATION
Exploited Cisco SD-WAN Manager flaw gives attackers admin API access
CISA added a critical Cisco Catalyst SD-WAN Manager authentication bypass to its KEV catalog with a three-day federal deadline and a required compromise check.
-
 ACTIVE EXPLOITATION
Two Citrix NetScaler zero-days under active attack, CISA and NCSC warn
CISA and the UK NCSC confirm attackers are exploiting two critical NetScaler ADC and Gateway flaws as zero-days. Check for compromise, then patch by 30 September.
-
 ACTIVE EXPLOITATION
CISA confirms exploitation of SharePoint and MikroTik RouterOS flaws
CISA added a SharePoint code injection flaw and a MikroTik RouterOS SSH bug that completes a known router takeover chain to KEV, with a 28 September deadline.
-
 ACTIVE EXPLOITATION
CISA flags six exploited flaws in VPN, SD-WAN and commerce platforms
CISA added six actively exploited CVEs in Check Point, F5 BIG-IP APM, Arista VeloCloud, WSO2 and Adobe Commerce to KEV this week, with deadlines of 25 and 27 September.
-
 ACTIVE EXPLOITATION
CISA confirms attacks on WordPress core file inclusion flaw
CISA added a WordPress core file inclusion bug that can lead to code execution to its KEV catalog, set a three-day federal deadline and required forensic triage.
-
 ADVISORY
FBI and CISA warn ICS integrators are a path into critical infrastructure
An FBI and CISA fact sheet cites an intrusion at a US industrial automation integrator where attackers packaged about 800 files, including customer SCADA data.
-
 LAW ENFORCEMENT
Operator of Rydox stolen-data marketplace pleads guilty in US case
A Kosovar national pleaded guilty to running Rydox, a marketplace that sold stolen US identities and cybercrime tools in over 7,600 transactions since 2016.
Attack types we report on
- Data breach
- An incident in which data is accessed or taken by someone not authorised to have it. A security breach does not always mean data left the network; a data breach does.
- Ransomware
- Malware that encrypts a victim’s files and demands payment for the key. Most crews now also steal the data first and threaten to leak it.
- Phishing
- A message that impersonates someone trusted to get the reader to open a malicious file, follow a link or hand over credentials. Spearphishing is the targeted version.
- DDoS
- A denial-of-service (DoS) attack floods or crashes a service so legitimate users cannot reach it. A distributed denial-of-service (DDoS) attack does it from many machines at once, usually a botnet.
- Supply chain
- An attack delivered through something the victim trusts, such as a software package, update or service provider, rather than against the victim directly.